



DUBLIN — AdSecure has released a report concerning trends in malicious online activity during the COVID-19 pandemic.
The company monitored malicious activity from March 1 to April 15, 2020 to see how the COVID-19 health crisis was being exploited by bad actors.
“As millions of people are now working from home, where online security isn’t as stringent compared to office cybersecurity systems, the pandemic has created a perfect storm for malvertisers,” the report begins.
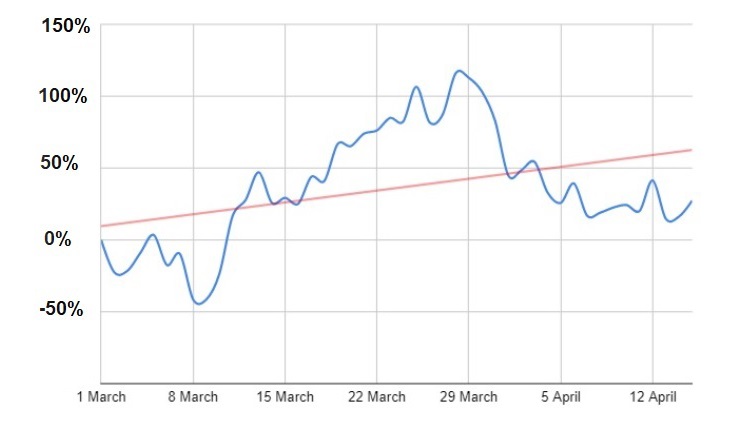
AdSecure concluded that malicious attacks grew exponentially alongside lockdowns and hit a peak of +116.14% on March 18.
This is the rest of AdSecure's report on “malvertisers”:
As lockdowns began to be introduced across the globe, the number of attacks increased dramatically.
The blue line represents the percentage rate of malvertising attacks based on comparing daily data with the number of attacks on March 1, and the red line represents the trend analysis.
We observed an increase in threats worldwide, particularly in the digital advertising ecosystems of prized “Tier 1” GEOs. Though subsiding somewhat from the massive spikes in late March, threat levels remain strong through the first half of April, with a more consistent, sustained pattern of attack, remaining significantly higher than levels detected during the first half of March.
Malvertiser’s Weapons of Choice
Malvertisers are using well-known logos — including the World Health Organization logo — to fool users into clicking on malware ads.
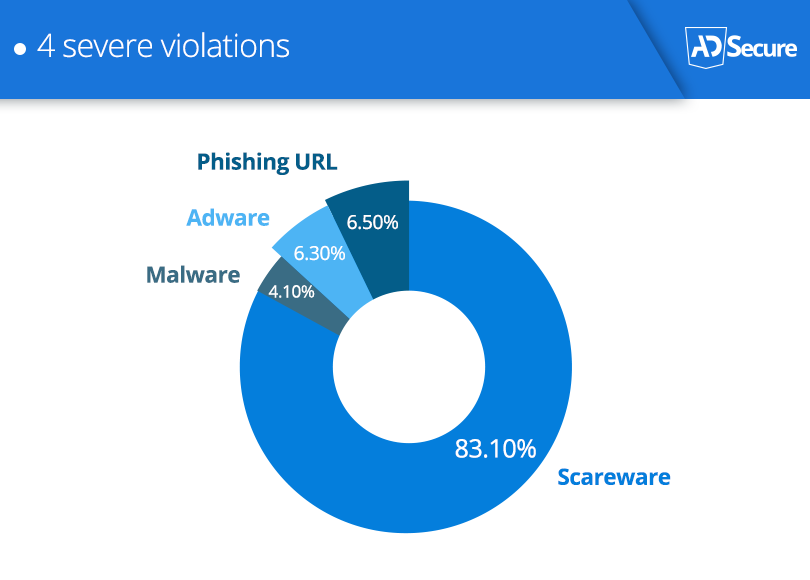
When analysing data on threat levels, we identified specific increases in the deployment of 4 types of malvertising attacks: Adware, Malware, Phishing Scams, and a very heavy use of Scareware attacks.
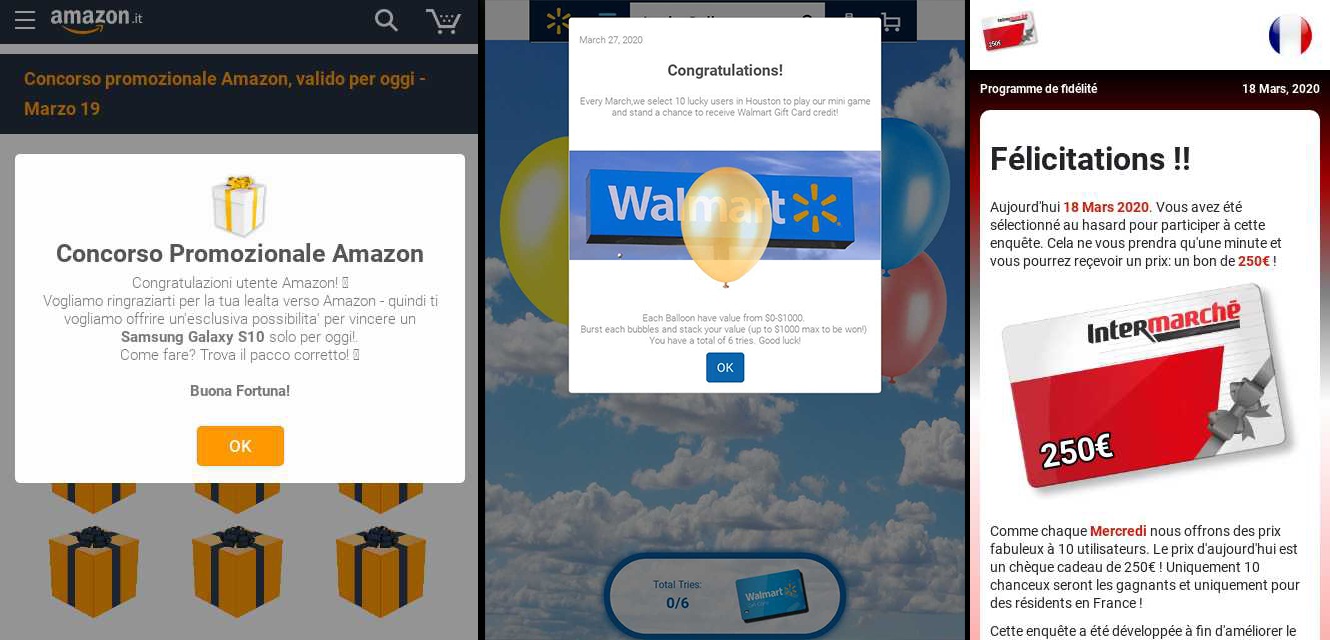
Many of these attacks made use of major branding that would be instantly familiar to their intended targets — phishing attacks leveraging fake Walmart offers in the US, Intermarche in France, and Amazon in multiple countries.
With the terms “Coronavirus”, “COVID-19”, and WHO (Word Health Organization) in the news constantly, malvertisers are using them to manipulate users, playing on their fears and anxieties to get them engaged with bad ads containing Malware.
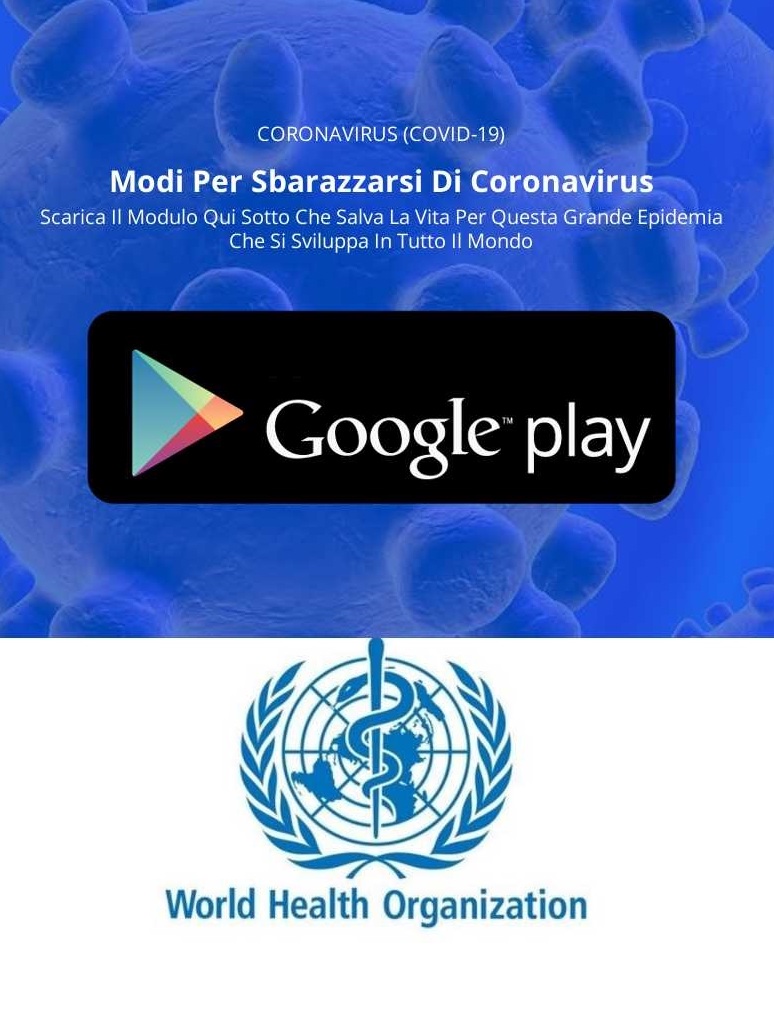
In the example below, AdSecure found a mobile banner ad in Italian, one of the countries worst hit by the pandemic. The ad delivers Malware via an auto-download, using the logo of the World Health Organization (WHO) and the GooglePlay logo to imply legitimacy.
The text translates to: “Ways to get rid of Coronavirus. Download the life-saving form here to stop this global pandemic.”
However, the text is not grammatically correct in Italian, so was obviously translated from another language — through Google Translate perhaps — so hopefully that deterred some end users from clicking on the banner ad.
Scareware Has Been the Preferred Choice of the Cybercriminal
Above all, the favourite attack delivery method during this spike in malicious activity appears to be Scareware, fake alerts claiming an imminent or existing threat to a user’s device — which of course does not exist — and is designed to trick the user for falling into a scam.
Scareware attacks grew exponentially, if we take the data from March 1 as the control, by March 4 there was a 485% increase by March 6 a 2,628% increase and by March 8 a 3,342% increase, where it remained at this new high right through to April 15.
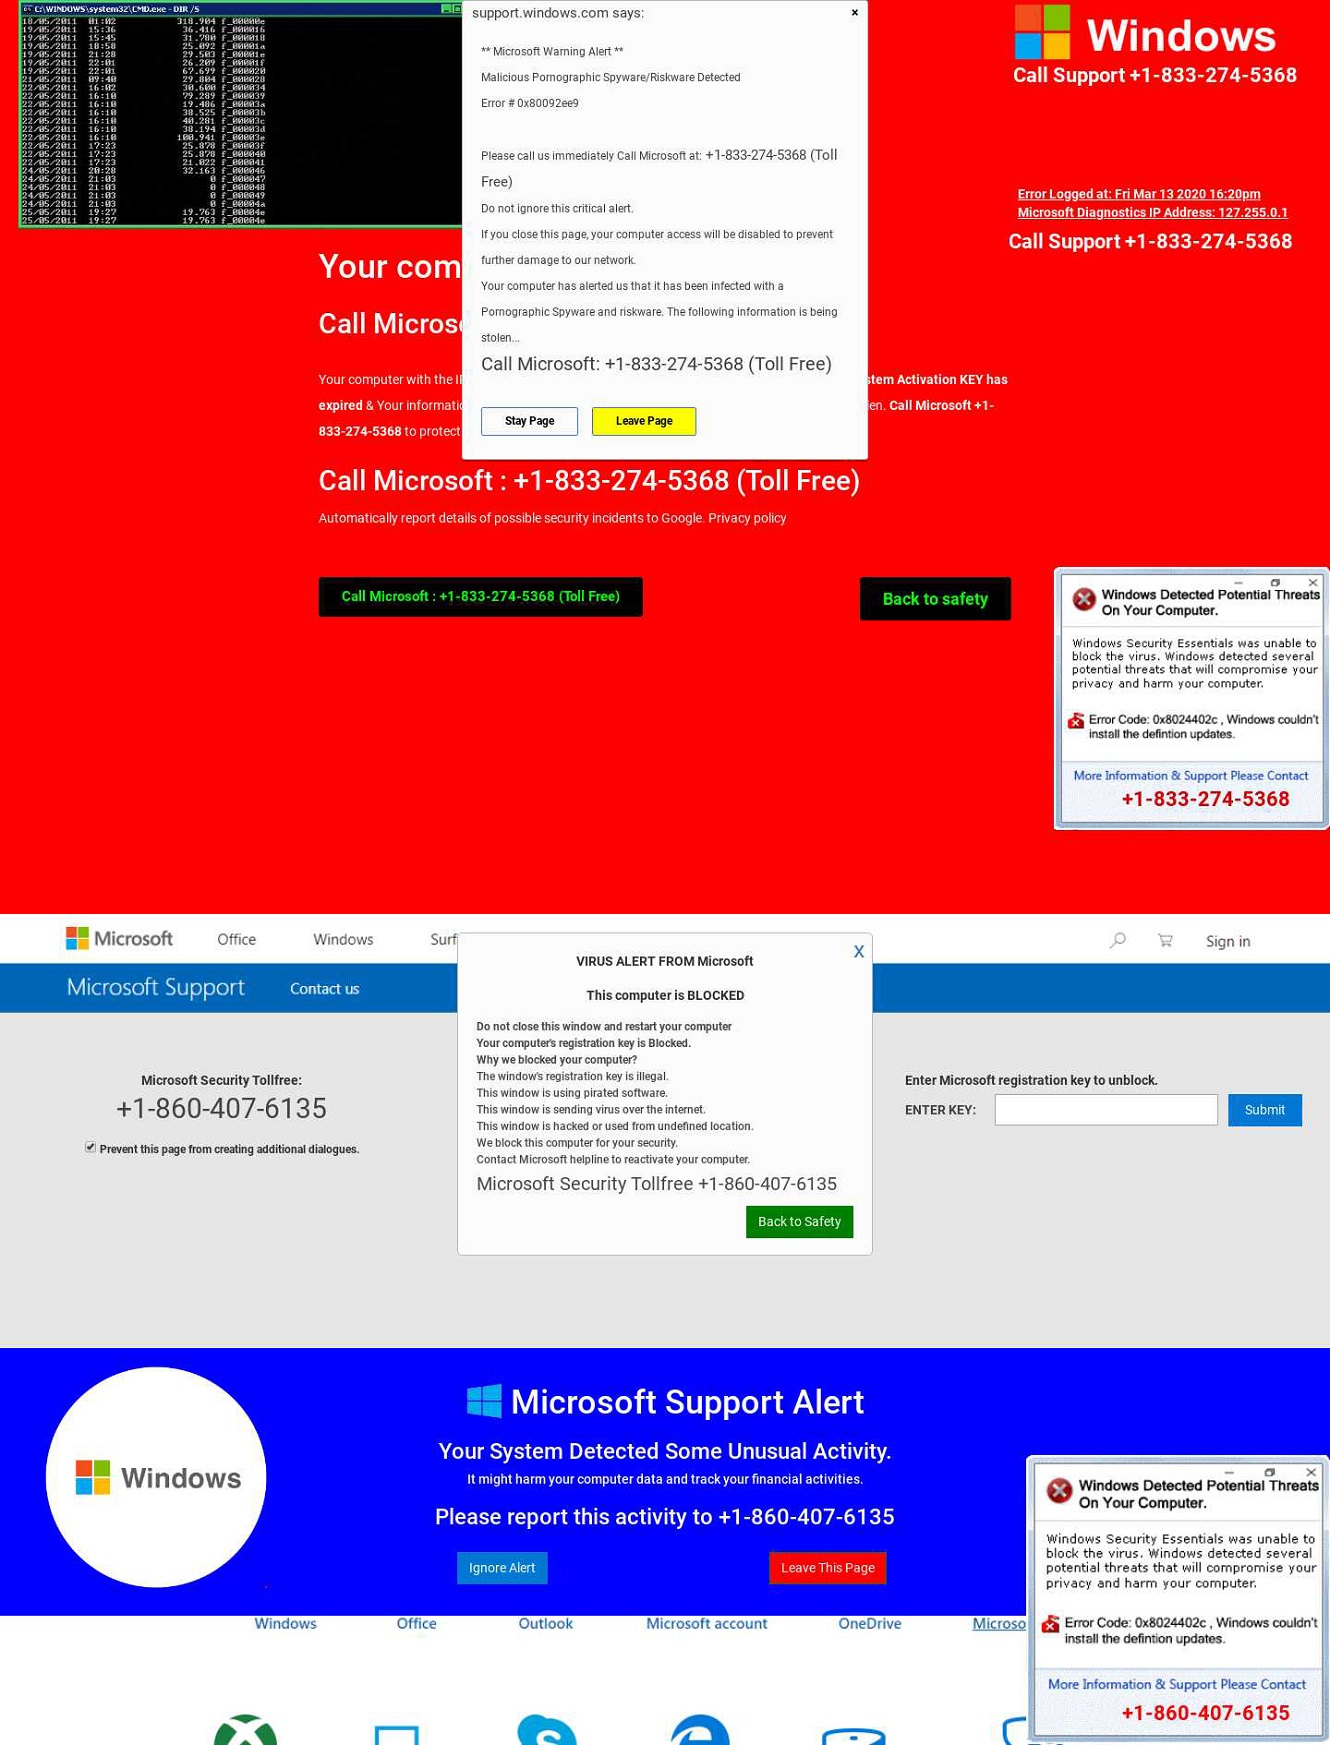
While the style and tone of Scareware attacks can vary, we often see these take the form of a tech support scam, wherein users are alerted that their system is infected with certain types of virus, or spyware.
Again, cybercriminals often rely on the iconography of well-known brands to imply legitimacy, convince users that they will indeed be contacting Microsoft technical support, as seen in the examples below:
Of course, the user isn’t contacting Microsoft, they’re falling into a trap.
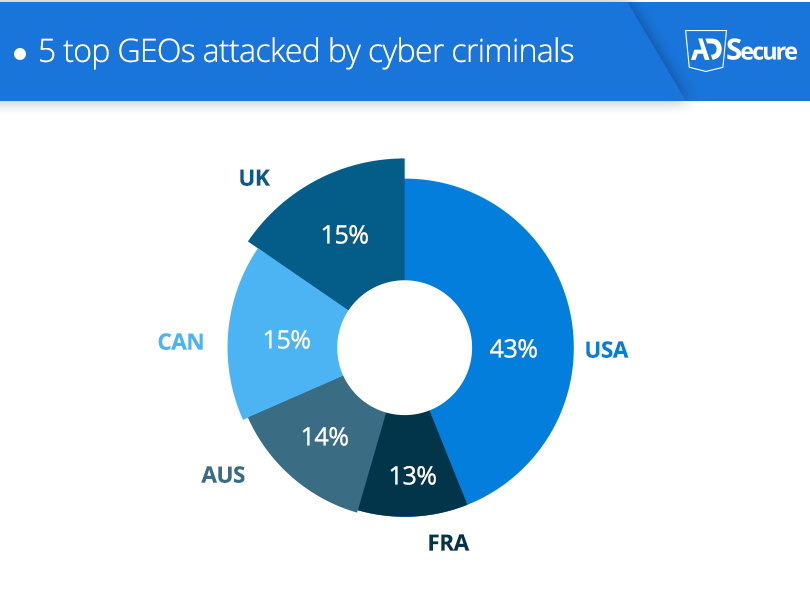
Bad Ads Surged Globally, but the U.S. Got Hit Particularly HardAdSecure examined which were the top 5 GEOs that received the highest malvertising attacks:
Tier 1 GEOs faced a wave of attacks with malvertisers heavily targeting the United States, with detected threats in the U.S. nearly 3x higher than in the other top 4 GEOs.
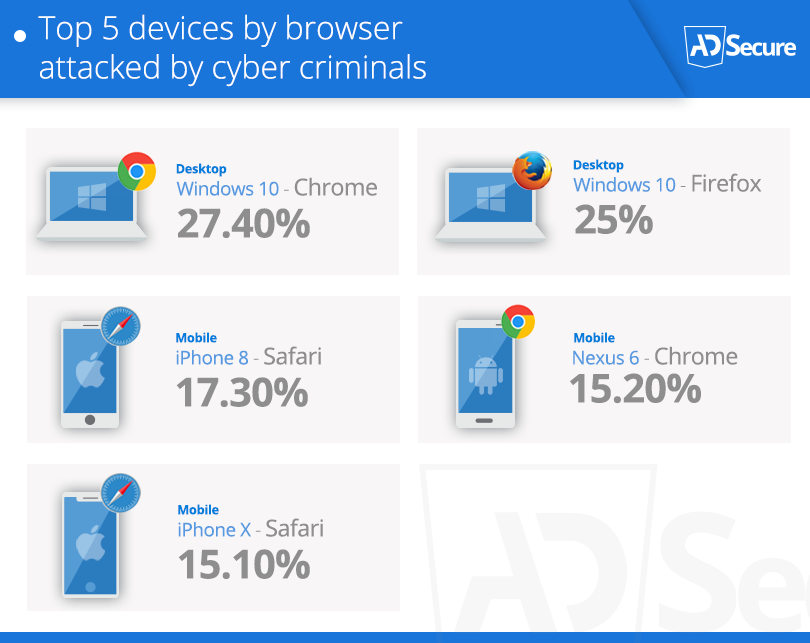
Windows PCs and iPhones Were Among Malvertisers’ Top 5 Device ChoicesWindows laptops and PCs came out on top as malvertisers attacked users working from home. For Apple users, the iPhone 8 and iPhoneX were top of the cybercriminal devices to attack.
AdSecure’s Sales Manager Bryan Taylor commented, “There isn’t much safety to be found in any particular device and browser combination, either, as throughout March and April we can see that threats are being detected consistently across multiple devices and browsers.”
With more people frequently browsing on both their desktop and mobile devices and using multiple browser options, Taylor added, “malvertisers can spread their attacks accordingly, maximizing the effective impact of each bad ad campaign they are running.”
“With this sustained increase in malicious activity within the digital advertising ecosystem,” Taylor continued, “it’s likely that as social distancing measures, and lockdowns continue while the world get’s a collective handle on the COVID-19 crisis, cybercriminals will continue to take advantage of the situation by deploying malicious ads, and it is vital that the industry remain vigilant in the fight against malvertising, particularly during the unprecedented times we all find ourselves in.”
“AdSecure is here to help publishers and ad platforms with the challenge of fighting malicious and poor quality ads while maintaining user safety and experience,” said a rep. “Our free trial account is available to anyone looking to #StopBadAds.”
To learn more, reach AdSecure at contact@adsecure.com.



